
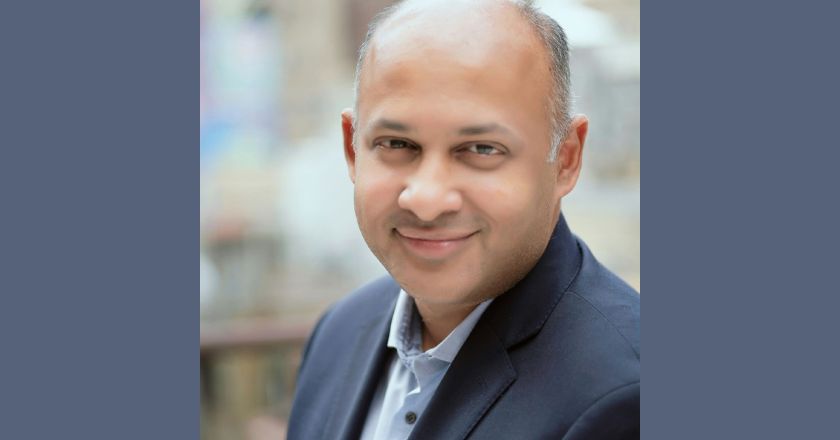
Piyush M, CEO of Data Dynamics, explains why data sovereignty has become critical to cybersecurity, resilience and the protection of sensitive information
Data sovereignty has moved beyond policy discussions and regulatory checklists. For governments and enterprises, it now sits at the centre of cybersecurity, operational resilience and public trust. Critical information, including citizen records, health data, tax files and identity credentials, increasingly resides within complex cloud environments. When that infrastructure is owned, operated or legally controlled by an overseas entity, questions arise about who can access the data, which laws apply and whether services can remain available during a major disruption.
Protecting personal information may involve external technology partners, but accountability cannot be outsourced. Data residency and data sovereignty are not the same, and conflating them has become one of the most consequential mistakes in enterprise architecture. Data can be stored on a server within national borders while remaining subject to foreign laws or accessible to operational teams based elsewhere.
Certain legislation can require providers incorporated in one jurisdiction to produce data stored in another. Globally distributed support and operations teams may also access tenant environments during maintenance or incident response, precisely when sensitive information can be most exposed.
Physical location alone does not establish legal or operational control. The Middle East has recognised this distinction more clearly than many regions. Saudi Arabia’s Personal Data Protection Law took effect in September 2023, with enforcement beginning a year later. It introduced requirements governing data localisation and cross-border transfers, with oversight from the Saudi Data and Artificial Intelligence Authority, linking data policy closely to the Kingdom’s wider AI ambitions. The UAE’s Personal Data Protection Law establishes requirements around consent, data processing and governance, while regulatory authorities continue to strengthen expectations for organisations handling sensitive information. Saudi Arabia has also explored concepts such as data embassies and sovereign digital sandboxes.
Qatar’s National Cyber Security Strategy 2024–2030 places data sovereignty among its priorities. The Abu Dhabi Global Market requires regulated firms to establish recovery objectives and demonstrate their ability to contain and respond to operational incidents. More than 140 countries have enacted data protection legislation, with many introducing provisions governing localisation and international transfers.
Data sovereignty is not a regional preference. It reflects a wider shift towards greater control, accountability and resilience.
Why does this matter for cyber risk rather than simply regulatory compliance? Three reasons stand out.
Concentration multiplies risk
When banking, logistics, healthcare and public services depend on a small number of shared platforms or availability zones, one technical failure, cyberattack, configuration error or regulatory restriction can create widespread disruption. Architecture designed around a single provider or jurisdiction can turn an isolated incident into a systemic problem. Organisations are therefore reassessing where critical workloads operate, how services are distributed and whether they can move data and applications when circumstances change. Sovereignty strengthens resilience by reducing excessive concentration and ensuring that organisations retain meaningful control over essential systems.
Opacity weakens defence
Heavy reliance on external cloud and operational technology providers can limit visibility and amplify third-party risk. Security teams cannot effectively protect environments when they lack access to telemetry, forensic evidence or the underlying control plane. A national computer emergency response team that cannot independently examine incidents, audit controls or obtain timely operational data is dependent on information supplied by vendors. That dependency can delay investigation, limit accountability and weaken response. Sovereignty of control gives authorised teams the visibility and authority needed to investigate threats, enforce policies and verify that security measures are working.
Personal data does not degrade gracefully
A compromised password can be reset. A leaked national identity record, biometric template or medical history cannot be meaningfully replaced. Citizens cannot change their fingerprints or reissue their health histories. Sensitive personal data is relatively inexpensive to copy but almost impossible to recover once exposed. That imbalance makes sovereignty a cybersecurity objective rather than a political preference. Organisations handling highly sensitive information must understand where the data resides, who can access it, which jurisdiction governs it and how it can be protected throughout its lifecycle.
The objections to localisation also deserve consideration. Local infrastructure can increase costs, fragment security tools and leave organisations dependent on a smaller pool of technical expertise. Localisation can also be misused to justify excessive surveillance rather than protect citizens. A poorly operated national cloud is not inherently safer than a well-managed international platform. Sovereignty pursued through complete technological isolation can create brittle, under-maintained systems and prevent organisations from benefiting from global threat intelligence and innovation. The answer is sovereignty of control, not isolation.
Organisations should classify workloads according to risk and sensitivity. Certain systems may require genuinely sovereign operations, while others may need contractual in-country residency. Less-sensitive workloads may remain suitable for standard cloud regions. Sensitive environments should use encryption keys controlled by the organisation and managed locally, independently of the underlying platform. In-jurisdiction operational staff should support the most critical workload tiers.
Contracts should include practical exit rights, data-portability provisions and clear responsibilities during incidents.
Those arrangements must also be tested. An exit strategy that exists only in contractual language offers little protection when an organisation needs to migrate systems or recover services quickly. Investment in domestic cybersecurity skills remains equally important. Sovereign infrastructure without sovereign expertise simply replaces one dependency with another. Governments and enterprises need professionals capable of operating, auditing and defending the systems entrusted with critical information.
Sovereignty in the technology stack is not nationalism applied to servers. It is recognition that control over data, infrastructure and legal access has become fundamental to security. The central questions are straightforward: Who can lawfully access the system? Who controls the encryption keys? Who can investigate an incident? Who determines where the data moves? Who can keep essential services running when the underlying environment is disrupted?
Countries and organisations that answer those questions deliberately will be better positioned to protect citizens, maintain trust and preserve operational resilience. Those that leave the answers to default settings may discover that control was surrendered long before a crisis revealed it.
This opinion piece is authored by Piyush M, CEO, Data Dynamics, Inc.
Source: Tahawul Tech