
AI is accelerating the speed and scale of cyberattacks, increasing pressure on organisations to move beyond reactive security practices. Defenders must identify exploitable weaknesses quickly, prioritise the exposures most likely to be targeted and strengthen oversight of emerging technologies such as generative AI and autonomous agents.
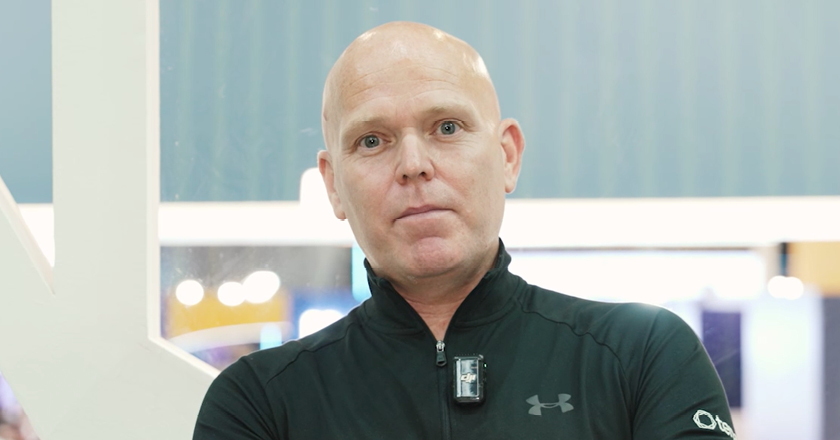
In an interview with TahawulTech.com, Gavin Millard, Vice President of Intelligence at Tenable, explains why exposure management has become critical to preventative cybersecurity. He also examines the risks created by shadow AI, poorly governed AI agents and phishing attacks, while outlining how Tenable’s AI-driven capabilities can help security teams operate at machine speed.
How will AI reshape cyberattacks and defence strategies over the next decade?
Attackers are already using AI to launch autonomous attacks at scale, and this trend will continue over the next decade. Security teams must move from human-speed processes to machine-speed operations if they are to defend effectively against increasingly automated threats.
AI can help defenders identify risks, prioritise exposures and respond much faster. Organisations must strengthen their ability to discover vulnerabilities and remediate the weaknesses most likely to be exploited by autonomous attackers.
Why has exposure management become essential for modern cyber defence?
Exposure management helps organisations shift from reactive security towards preventative defence. Security teams need a clear understanding of their assets, vulnerabilities and exposures across the environment.
The priority is to find exposures quickly, fix them even faster and focus resources on the relatively small number of weaknesses that attackers are most likely to exploit. Such an approach helps organisations reduce risk before an attack succeeds.
What security gaps are emerging as enterprises adopt AI tools and autonomous agents?
Shadow AI represents a significant and often overlooked data-loss risk. Employees may share sensitive information with generative AI tools to improve a spreadsheet or presentation, allowing corporate data to leave the organisation’s controlled environment.
Autonomous agents also create identity and access risks. Agents are often deployed without secure controls governing their permissions, access and ability to execute actions. Organisations also need mechanisms to audit an agent’s reasoning and decision-making. Without such safeguards, AI agents can operate beyond intended boundaries and introduce considerable risk.
How should organisations address phishing without placing responsibility on employees?
Blaming an employee for clicking a phishing link overlooks the underlying failure of the organisation’s security controls. Security teams should identify and restrict the channels through which phishing links enter the environment and ensure that malicious links cannot successfully connect to their intended destinations.
Organisations should also address the vulnerabilities and exposures targeted by phishing campaigns. Protecting browsers, identities, endpoints and connected systems is more effective than attributing blame to individual employees.
How do Hexa AI, AI Exposure and the Cyber Agents Exchange support defenders?
Hexa AI and the Cyber Agents Exchange bring together AI capabilities developed to support security teams. Agents can be shared, used and contributed by participants, allowing the wider security community to benefit from tools created by individual contributors.
AI Exposure focuses on inventory and visibility. Organisations need to know which AI tools have been deployed and how employees are using them. Visibility forms the first line of defence because security teams cannot protect technologies or assets they do not know exist.
What closing advice would you give organisations strengthening their cyber resilience?
Find exploitable exposures fast and fix them faster.
Image Credit: Tenable
Source: Tahawul Tech