
Critical infrastructure organisations face growing exposure to advanced, AI-enabled and file-borne threats as operational environments become increasingly connected. Effective protection requires purpose-built security controls capable of sanitising files, securing transfers and preventing sensitive information from leaving isolated networks.
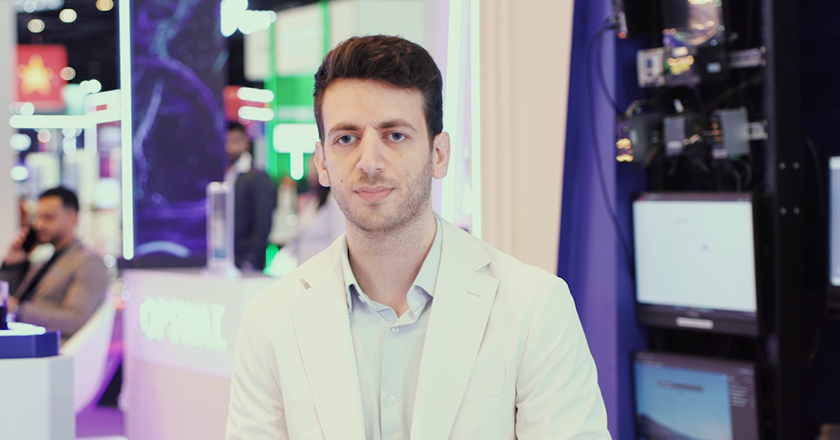
In an interview with TahawulTech.com at GISEC Global 2026, Saif Alrefai, Solutions Engineering Director for the Middle East at OPSWAT, discusses how Deep Content Disarm and Reconstruction, MetaDefender and unidirectional security gateways support zero-trust file transfer. Alrefai also explains why organisations must strengthen fundamental security controls before introducing AI-driven automation.
How did your experience at GISEC Global 2026 compare with previous editions?
GISEC Global 2026 has been highly productive for OPSWAT. We have held valuable meetings with partners and customers, and we are pleased to participate in the event again. It continues to provide an important platform for engaging with the regional cybersecurity community and discussing critical infrastructure protection.
How does OPSWAT use deep content inspection and file sanitisation to prevent advanced threats from reaching critical infrastructure environments?
OPSWAT uses Deep Content Disarm and Reconstruction (Deep CDR) to mitigate file-borne threats, including advanced, AI-generated and AI-enabled attacks. Rather than relying solely on threat detection, the technology applies a zero-trust approach to file security.
Potentially malicious or harmful content is removed from each file before it enters a critical network or infrastructure environment. This process enables organisations to use clean, sanitised files without exposing sensitive systems to embedded threats.
How does OPSWAT secure data transfers between IT and OT environments while maintaining operational availability and protecting air-gapped networks?
OPSWAT secures the complete file-transfer process. Files are first scanned and sanitised through the MetaDefender platform to ensure they are safe to use. Once sanitisation is complete, files can be transferred into an air-gapped network through OPSWAT’s NetWall unidirectional security gateway, or data diode. The technology permits data to move in one direction while preventing information from travelling back out. This approach protects restricted environments while allowing critical operations to continue without disruption.
What should enterprises consider when selecting technology to protect critical networks?
Enterprises should choose purpose-built technologies designed specifically for critical infrastructure environments. Generic cybersecurity tools may not always be suitable for specialised IT and OT networks or the operational conditions in which they function.
Technology selection should reflect the organisation’s environment, risk profile and operational requirements. Controls must provide strong protection without disrupting essential services.
How can enterprises balance traditional security tools with AI-based technologies?
AI can strengthen security workflows and improve automation, but organisations should not overlook cybersecurity fundamentals. Strong security controls, zero-trust architecture and clearly defined processes must form the foundation of the security strategy.
Once those fundamentals are in place, enterprises can introduce AI-driven automation more effectively. The right balance combines established security practices with AI capabilities that build upon a resilient and well-governed architecture.
What is your message to the regional cybersecurity community from GISEC Global 2026?
GISEC Global provides an important opportunity for the cybersecurity community to connect, exchange ideas and explore ways to strengthen critical infrastructure protection. I encourage regional organisations, partners and security professionals to engage with OPSWAT and discuss how we can work together to protect critical environments.
Image Credit: OPSWAT
Source: Tahawul Tech