
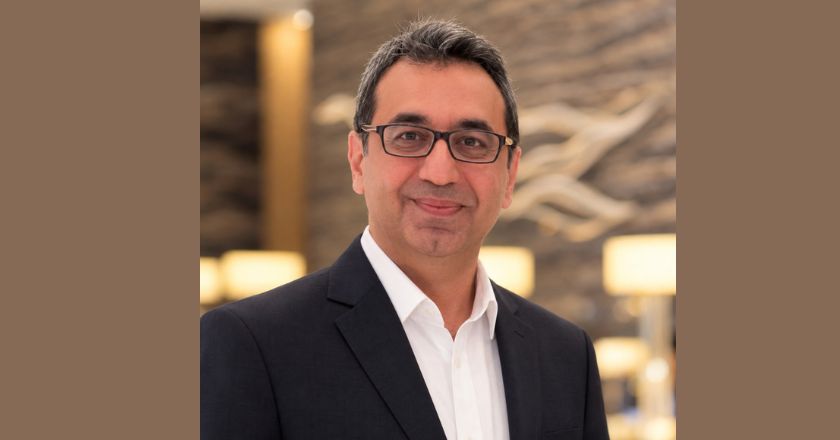
Harish Chib, Vice President for Emerging Markets, Middle East & Africa at Sophos, discusses critical infrastructure protection, AI-led security operations, managed services and regional expansion
Cyber resilience now extends beyond preventing attacks to maintaining operations during active incidents. Organisations must secure interconnected IT, operational technology, cloud, identity and third-party environments while responding to threats at greater speed.
In an interview with TahawulTech, Harish Chib, Vice President for Emerging Markets, Middle East & Africa at Sophos, discusses layered defence, managed detection and response, governed AI autonomy and human oversight. He also explains how managed service providers can help under-resourced businesses strengthen their security posture and outlines Sophos’ priorities for the Middle East.
Interview excerpts
What does effective cyber resilience look like for organisations operating across the GCC’s critical infrastructure sectors?
Cyber resilience in critical infrastructure is no longer limited to preventing attacks. Organisations must also maintain operational continuity and continue serving customers and suppliers while an active incident is being investigated and contained. Effective resilience requires a layered defence that enables organisations to prevent, detect, respond to and recover from cyber incidents. Continuous visibility must extend beyond conventional IT assets, such as laptops and servers, to operational technology, cloud platforms, identities and connected third-party environments across the supply chain. Speed and accountability are particularly important in high-impact sectors.
AI can accelerate investigation, triage and response, but human oversight remains essential when decisions involve significant operational or business risk.
How is Sophos helping under-resourced SMBs and mid-market organisations address the region’s cybersecurity skills gap?
Cyberattacks do not distinguish between large enterprises and smaller businesses. SMBs and mid-market organisations, however, often lack the budgets and specialist skills required to employ dedicated CISOs, build security operations centres or maintain separate infrastructure, application, and cybersecurity teams. Sophos helps bridge this gap through managed security services, including services delivered through its partner ecosystem. The objective is to reduce the operational burden on lean IT teams by providing continuous protection, detection and response. Advisory services also help organisations address governance and compliance requirements, including the need for independent assessments. These capabilities are integrated through the Sophos platform, giving customers access to operational security and practical guidance without having to build every capability internally.
How much SOC decision-making is now AI-driven, and where should human oversight remain essential during high-stakes incidents?
Sophos uses AI to help security teams manage the speed and scale of modern threats, correlate signals and deliver high-confidence responses. Repeatable tasks with well-understood patterns can be assigned to agentic AI systems, enabling investigations and responses to take place within seconds. Human expertise remains essential for complex, unfamiliar or novel incidents. Analysts must also remain involved whenever a decision could create substantial business impact or requires a deeper understanding of operational context. Our guiding principle is governed autonomy. Tested, repeatable and clearly bounded processes can be automated, while high-risk decisions retain human oversight.
The model remains AI-led with humans in the loop rather than fully autonomous.
Which cybersecurity challenges are driving organisations towards MSPs, and how are providers adapting their services?
MSPs were traditionally expected to deliver technology-focused operational outcomes, including infrastructure management and application maintenance. Expectations are now expanding because many SMBs and mid-market organisations lack dedicated cybersecurity leaders and specialist security teams. Customers increasingly want MSPs to act as trusted cybersecurity advisers and, in some cases, serve as de facto CISOs. This shift allows MSPs to support governance, reporting, security assessments and incident response alongside their traditional technical services. Sophos provides MSPs with a platform and dedicated training resources to support this transition. Training covers advisory services and effective responses during active cyber incidents. Upskilling and reskilling help MSPs evolve from technical service providers into strategic cybersecurity partners.
What are Sophos’ main business priorities for the Middle East over the next six months?
Sophos remains committed to expanding its presence in the Middle East. Current plans include growing the regional team, expanding enterprise capabilities and exploring the establishment of a local security operations centre when conditions make the investment feasible. AI-native security capabilities, managed detection and response, and stronger support for MSPs will remain key priorities. Sophos also plans to help organisations achieve practical resilience through unified visibility across their security controls, stronger prevention and detection, and faster incident response. Further investment in the partner ecosystem will help organisations adapt their security programmes as regional cyber risks evolve. These priorities are intended to strengthen protection for enterprises while enabling MSPs to support SMB and mid-market customers more effectively.
Source: Tahawul Tech