
Naman Taldar of Rockwell Automation explains why asset visibility, risk-based investment, and proactive security programmes are critical to protecting industrial operations
Artificial intelligence is accelerating cyber threats across operational technology environments by making sophisticated attack techniques more accessible and scalable. Industrial organisations must also contend with ageing assets, fragmented architectures, limited visibility and the potentially severe operational and financial impact of plant downtime.
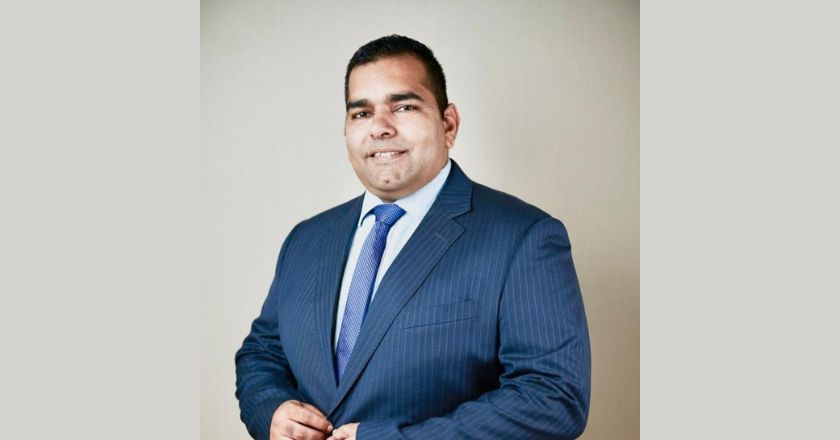
In this interview, Naman Taldar, Regional Lead – OT Cybersecurity at Rockwell Automation, discusses how organisations can strengthen asset visibility, adopt proactive risk-based security programmes and align cybersecurity investment with operational resilience. Responsible for OT cybersecurity consulting and business development across the Middle East, Turkey and Africa, Taldar brings more than 15 years of IT and OT industry experience, including work on critical infrastructure and defence projects.
Interview excerpts
How is AI lowering the barrier to attacking operational technology (OT) systems?
Artificial intelligence is changing the economics of cyberattacks. Historically, targeting industrial environments required specialised knowledge of operational technology, industrial protocols and plant operations. Today, AI can help automate many aspects of reconnaissance, vulnerability research, social engineering and malware development, allowing less sophisticated threat actors to conduct more advanced attacks. AI can also accelerate the speed at which attackers identify weaknesses, generate convincing phishing campaigns, or adapt malware to different environments. For industrial organisations, that means threats can emerge faster and at greater scale than in the past. At the same time, AI is not creating entirely new risks. It is amplifying existing ones. Many OT environments still contain aging assets, fragmented architectures, and systems that were not originally designed with cybersecurity in mind. As a result, organisations should focus less on specific AI-driven attack scenarios and more on strengthening cyber resilience overall. That means improving visibility, reducing vulnerabilities, implementing defense-in-depth strategies, and ensuring they can detect, respond to, and recover from incidents quickly.
How important is asset visibility in managing OT cyber risk, and why do organisations continue to struggle with understanding what is actually connected within their industrial environments?
Asset visibility is foundational to any effective OT cybersecurity program. Before an organisation can assess risk, prioritise investments or respond to threats, it must understand what assets exist within the environment and how those assets interact. The challenge is that industrial environments are often a diverse mix of many solutions. Very often, facilities operate equipment from multiple vendors spanning several decades. Assets may have been added during expansion projects, inherited through acquisitions, or maintained by different teams over time. In many cases, documentation has not kept up with operational changes. Unlike traditional IT environments, OT assets often include controllers, drives, sensors, engineering workstations and other specialised devices that are not always visible through conventional IT security tools. As connectivity increases across plants and enterprises, maintaining an accurate asset inventory becomes even more difficult. Without comprehensive visibility, organisations may not know which systems are vulnerable, outdated or critical to production. Asset visibility therefore becomes the basis for risk prioritisation, vulnerability management, compliance efforts and incident response planning.
“Organisations cannot effectively protect assets they do not know they have.”
How can organisations move from a reactive approach to OT cybersecurity toward a more proactive, risk-based security program?
Too often industrial organisations still take a reactive approach to cybersecurity, addressing issues after vulnerabilities are discovered or incidents occur. While that may reduce immediate problems, it is not sufficient in today’s threat environment. A more mature approach begins with understanding business risk rather than focusing solely on technology. Organisations should identify their most critical assets, evaluate potential operational impacts, and prioritise security investments based on those risks. This requires a structured program built around continuous assessment, vulnerability management, governance, monitoring and incident preparedness. International frameworks such as IEC 62443 and NIST provide valuable guidance because they help organisations establish repeatable processes for improving security maturity over time. Proactive cybersecurity is also about recognising that risk cannot be eliminated completely. The goal is to continuously identify, quantify and prioritise risks so that limited resources are focused on the areas that will have the greatest impact on operational resilience.
Organisations that treat cybersecurity as an ongoing lifecycle program, rather than a series of isolated projects, are typically better positioned to reduce risk and maintain business continuity.
How should the potential cost of plant downtime influence OT security spending?
Downtime is often one of the most important factors when evaluating OT cybersecurity investments. While cybersecurity discussions sometimes focus on technical indicators such as vulnerabilities or alerts, industrial organisations ultimately measure risk in terms of operational consequences. A cyber incident can disrupt production, delay deliveries, impact product quality, compromise safety and create regulatory or contractual challenges. For many industrial operators, even a short interruption can result in costs that significantly exceed the investment required to strengthen cybersecurity controls beforehand. This does not mean organisations should pursue cybersecurity spending without limits. Rather, security investments should be evaluated against the potential operational and financial impacts of disruption. The most effective programs are those that connect cybersecurity priorities directly to business objectives such as availability, safety, productivity and resilience.
“When cybersecurity is viewed through the lens of operational continuity, it becomes easier to justify initiatives that improve visibility, reduce exposure to threats, enhance monitoring and accelerate recovery after an incident.”
What balance should companies maintain between investing in OT cybersecurity and managing operational costs?
Organisations should avoid viewing cybersecurity and operational efficiency as competing priorities. In industrial environments, they are increasingly interconnected. The most successful organisations focus on risk-based investment strategies. Instead of attempting to address every possible threat, they identify the areas of greatest operational significance and direct resources accordingly. This allows them to improve security while maintaining financial discipline. Organisations should also recognise that cybersecurity spending is not limited to technology purchases. Investments in governance, staff training, asset management, incident preparedness and managed security services can often deliver significant value and help address resource constraints.The objective is not to achieve perfect security. The objective is to build resilient operations that can continue to function safely and productively despite a constantly evolving threat landscape. When cybersecurity investments are aligned with operational priorities, regulatory requirements, and business risk, organisations are better positioned to protect both their operations and their long-term competitiveness.
Source: Tahawul Tech